In this post we’ll break down why some vendors calling their ‘VM plus dashboard’ setups “cyber ranges” are missing the mark and misleading customers, and what a real cyber range environment brings to the table.
What a Cyber Range is NOT...
❌ Just VMs with a pretty UI. Spinning up virtual machines behind a basic dashboard doesn’t magically give you realistic attack simulations or user behaviors—it’s still just infrastructure.
❌ A fancy vulnerability scanner. Yes, scanning for holes is important, but you’re not practicing defense if you only see a list of findings and never face an actual exploit in action.
❌ A locked-down tutorial. Canned exercises where you click “next” and follow step-by-step instructions feel more like a lab manual than a live-fire exercise.
❌ A log or compliance dashboard. Charts and reports are great for oversight, but they don’t let you test detection and response under pressure.
❌ A one-and-done network snapshot. If you never change the network, rotate in new threats, or spin up fresh attacks, you’re not training for tomorrow’s challenges—you’re just revisiting yesterday’s incidents.
What a Cyber Ranges REALLY IS...
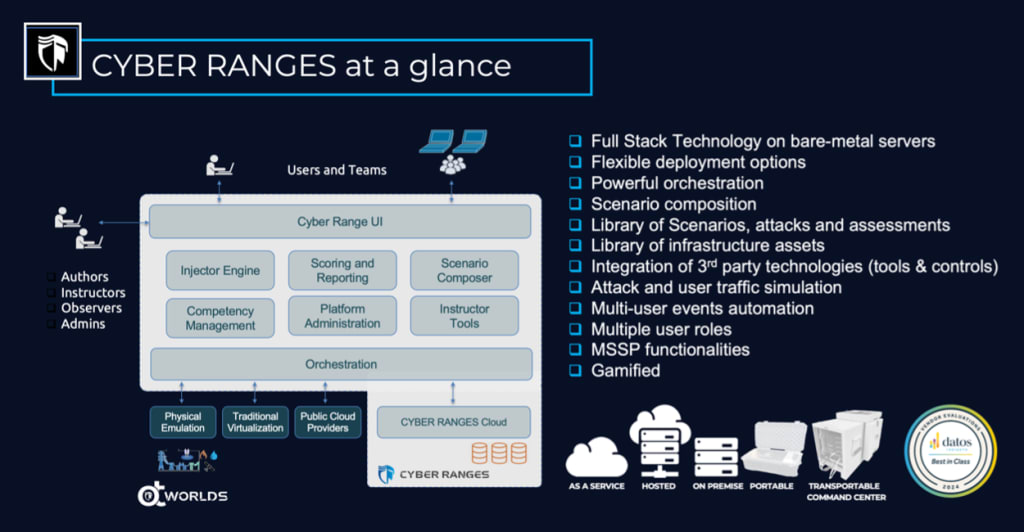
A deep-dive, engaging, experiential, interactive playground. Think full networks (IT and OT), services, user traffic and even insider behaviors—all orchestrated so you can practice defending against real-world threats.
Flexible simulation and emulation. You can simulate network protocols in software, emulate actual hardware/software stacks, or mix virtual and physical gear to match your needs.
Automated build and teardown. Behind the scenes there’s a smart engine provisioning, configuring, and tearing down your environment on demand—so you can run dozens of scenarios without manual toil.
Live threat injection and telemetry. Want to unleash a ransomware campaign? Spoof phishing emails? Inject malicious traffic? It’s all timed and tunable—and every click, packet, and alert is tracked for debrief.
Built-in training and scoring. Integrated learning modules quiz you, score your team, track progress, and let instructors finetune challenges or let learners go at their own pace.
Red-team vs. Blue-team vs. Purple-team. Host full adversary-emulation exercises, fortify defenses, then collaborate to close gaps—so you’re not just playing defense, you’re learning the attacker’s playbook.
More reading at:
https://cyberranges.com/mapping-cyber-ranges-to-gartners-product-performance-framework/
https://cyberranges.com/cyber-ranges-leading-the-future-of-preemptive-cybersecurity/
https://cyberranges.com/cyber-ranges-injector-engine-latest-version-overview/
https://cyberranges.com/effective-cyber-drills-must-mirror-the-realities-of-the-battlefield/
